Analysis · artificial intelligence
Pythie
The AI that links events to rebuild the attack, and explains its verdict.
Sequence
Step by step
It receives
Alerts and events, from NOX or another tool.
It links
Which process launched what, and where it went.
It assesses
Attack or not, and how confident it is.
It explains
The reasons behind the verdict, so you can check.
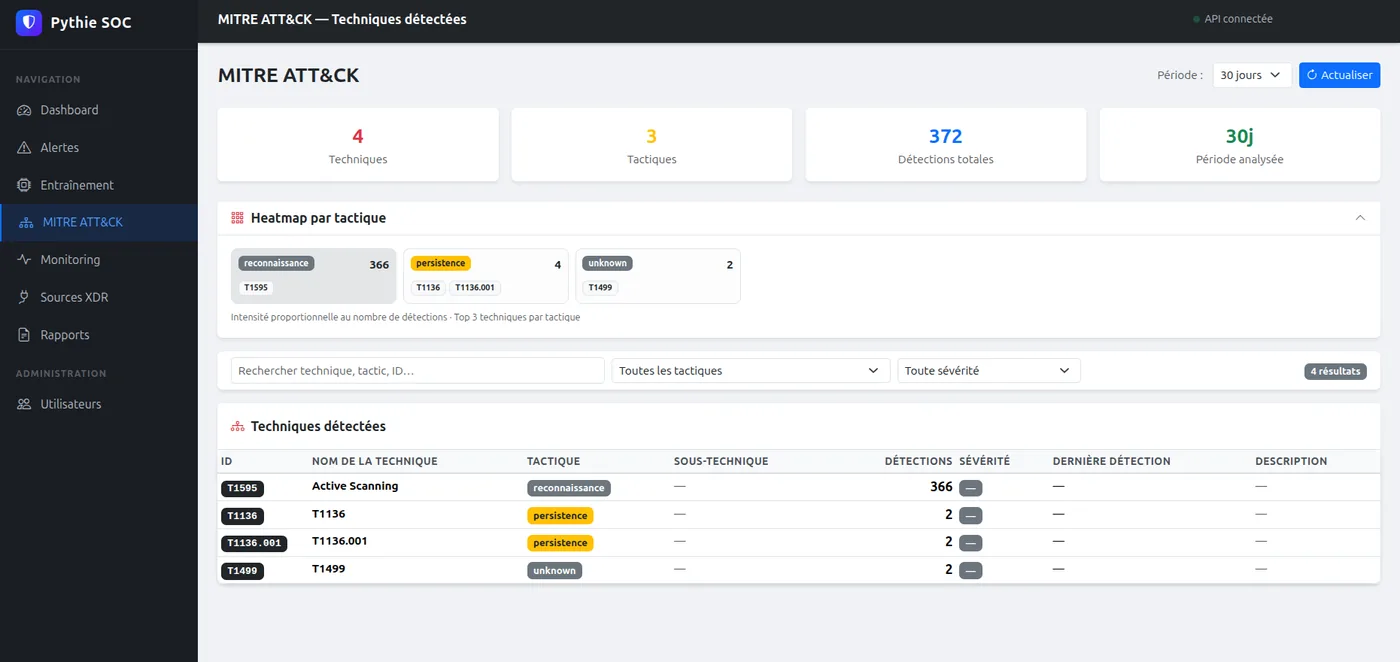
Techniques
The attacker's tactics, grouped.
- MITRE ATT&CK mapping
- Over 30 days or more
- Works with other SIEMs
Sovereignty
An AI that stays in your country
Hosted in your country
In line with the laws in force.
Only what is needed
It only receives the alerts to analyze, encrypted.
The analyst decides
Pythie advises, your threshold decides.
Questions about Pythie
Does it work without NOX?
Yes, it can also analyze other tools. NOX remains the richest source.
Where is Pythie hosted?
In your country, in line with the laws in force. Only the alerts to analyze are sent to it, encrypted.
Can it be wrong?
Yes. That is why it explains every verdict.